A CISO’s Guide to Vendor, SaaS, and Supply Chain Security
Explore the top third-party attack vectors of 2025, with practical defenses, warning signals, and playbooks for strengthening third-party risk management.
Download whitepaperMerqab resource library
Research, product detail, and practical checklists for teams building a more connected third-party risk program.
Selected resources

Explore the top third-party attack vectors of 2025, with practical defenses, warning signals, and playbooks for strengthening third-party risk management.
Download whitepaper
Understand DORA’s requirements for ICT risk management, third-party oversight, incident reporting, and resilience testing ahead of the 2025 compliance deadline.
Download whitepaperBrowse the library

A practical framework for assessing vendor risks, prioritizing findings, applying quantitative and qualitative methods, and maintaining continuous monitoring.
Download whitepaper
An examination of 26 major data breaches across industries, including third-party incidents, ransomware, unauthorized access, and their financial impact.
Download whitepaper
A comprehensive guide to categorizing third-party risks, protecting critical vendors and cloud providers, and supporting business continuity.
Download whitepaper
Move beyond activity counts with board-ready KPIs that prove risk reduction and track accountability, closure, and resilience across your third-party program.
Download checklist
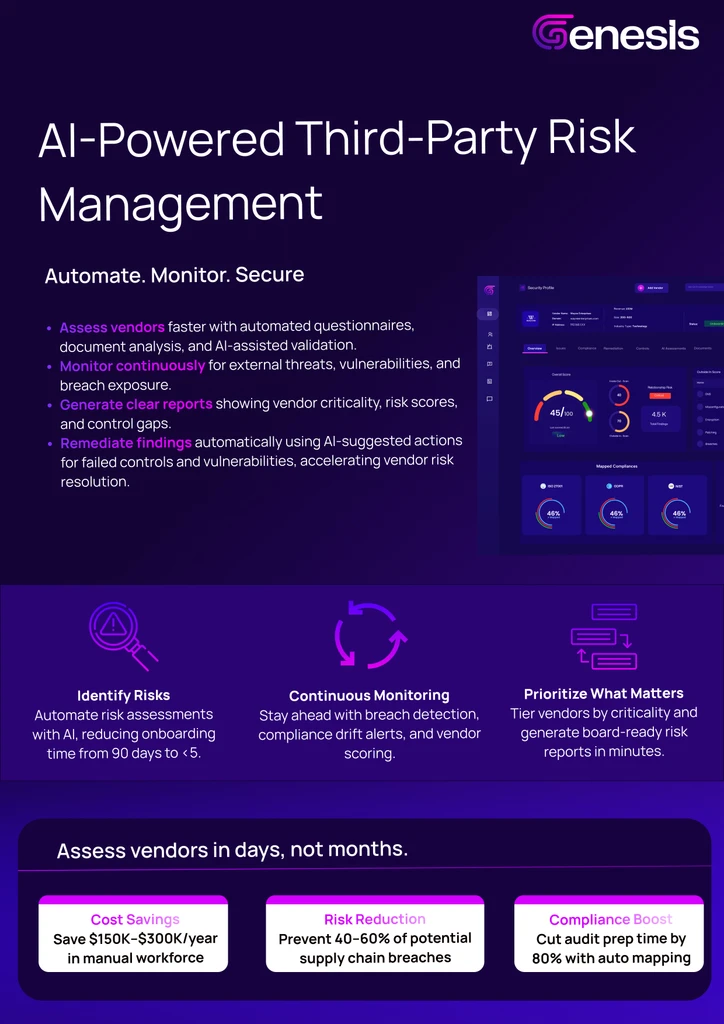
Automate vendor risk assessments, continuously monitor external threats, generate board-ready reports, and accelerate remediation with AI-assisted workflows.
Download datasheet
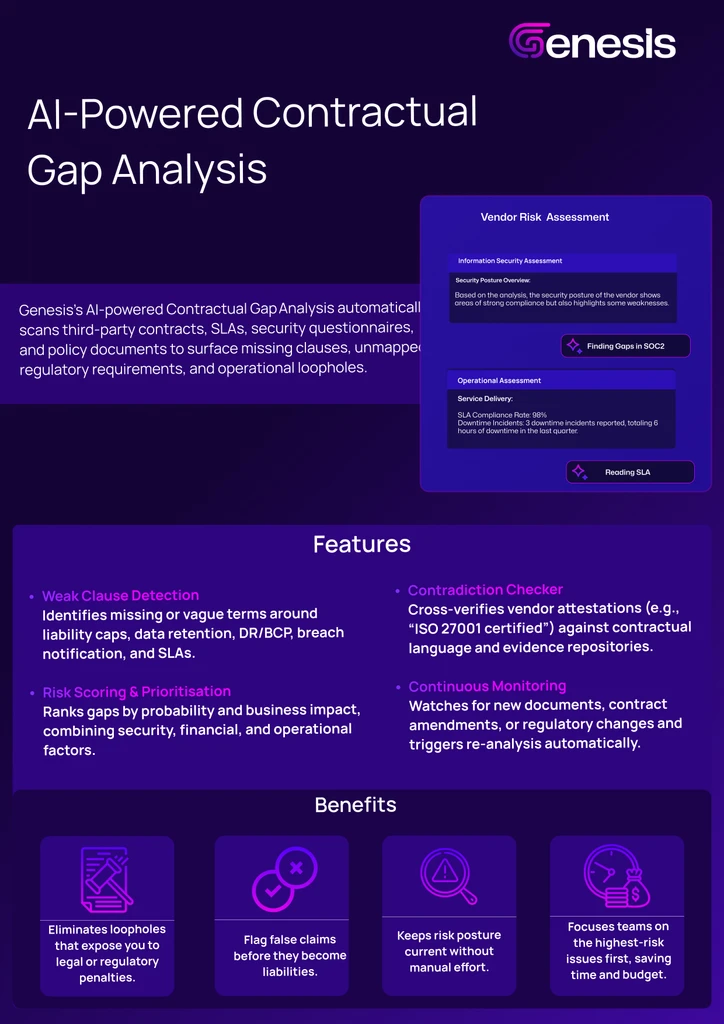
Scan contracts, SLAs, policies, and questionnaires to identify missing clauses, contradictions, compliance gaps, and operational risks within minutes.
Download datasheet
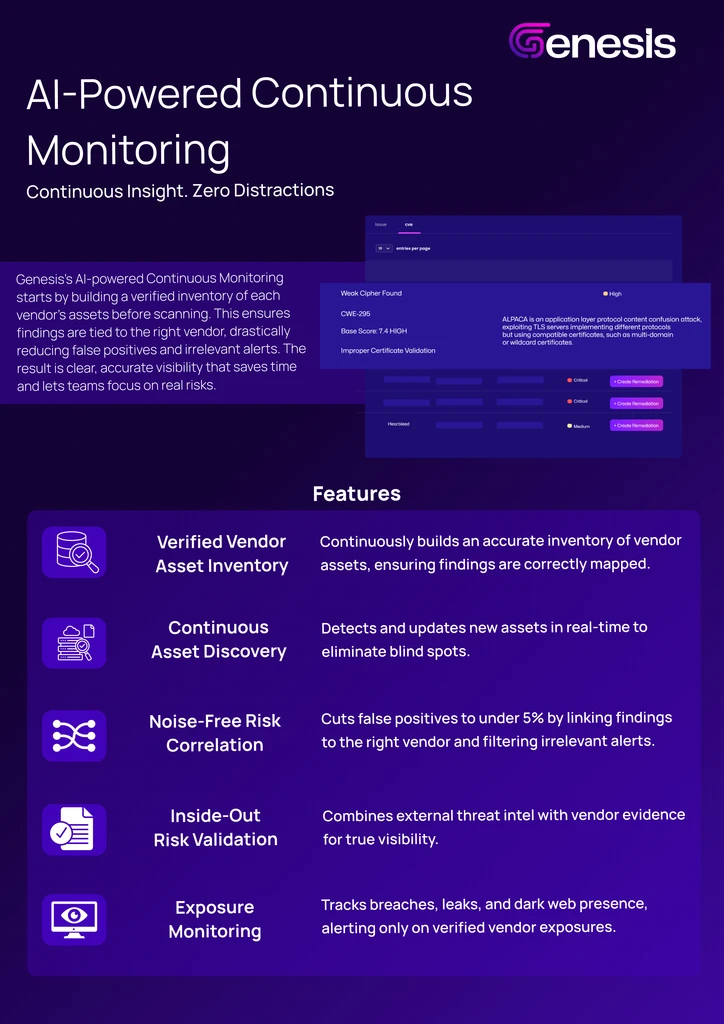
Build a verified vendor asset inventory, discover exposures continuously, reduce false positives, and connect external threat intelligence to vendor evidence.
Download datasheet