Intelligence beyond the knownExplore Event Horizon
Merqab

Merqab intelligence

Signals worth following.

Clear thinking on cyber risk, resilience, and the decisions between.

Latest intelligence

Understanding The Saudi Cybersecurity Workforce Framework (SCyWF)

Understanding The Saudi Cybersecurity Workforce Framework (SCyWF)

Khalifa Al ShehhiKhalifa Al Shehhi

July 2025 · 9 min read

Discover how the Saudi Cybersecurity Workforce Framework (SCyWF) is shaping the Kingdom’s cybersecurity landscape by defining clear roles, skill requirements, and structured pathways to build a resilient, future-ready cybersecurity workforce aligned with Vision 2030.
Understanding Saudi Arabia NCA’s Essential Cybersecurity Controls (ECC)

Understanding Saudi Arabia NCA’s Essential Cybersecurity Controls (ECC)

Khalifa Al ShehhiKhalifa Al Shehhi

July 2025 · 10 min read

Learn about Saudi Arabia’s NCA Essential Cybersecurity Controls (ECC), a structured framework helping organizations strengthen cybersecurity, ensure compliance, and manage cyber risks effectively.
What is SAMA Cyber Security Framework and How Does it Impact Third-Party Risk Management (TPRM) in Saudi Arabia?

What is SAMA Cyber Security Framework and How Does it Impact Third-Party Risk Management (TPRM) in Saudi Arabia?

Khalifa Al ShehhiKhalifa Al Shehhi

June 2025 · 7 min read

Discover how the SAMA Cybersecurity Framework influences Third-Party Risk Management (TPRM) in Saudi Arabia, with insights into mandatory controls, vendor compliance, and maturity level requirements for financial institutions.

NIST Cybersecurity Framework 2.0 and Its Impact on Third-Party Risk Management

NIST Cybersecurity Framework 2.0 and Its Impact on Third-Party Risk Management

Tanay RaiTanay Rai

June 2025 · 6 min read

Explore how NIST CSF 2.0 reshapes third-party risk management with new governance, supply chain controls, and maturity tiers for cybersecurity resilience.

AI-Driven Contractual Gap Analysis for TPRM.

AI-Driven Contractual Gap Analysis for TPRM.

Tanay RaiTanay Rai

June 2025 · 4 min read

Discover how AI-powered gap analysis transforms third-party risk management, identifying compliance gaps quickly and efficiently for smarter decisions.

Third-Party Cyber Risk Management in Banking

Third-Party Cyber Risk Management in Banking

Syed AmozSyed Amoz

May 2025 · 5 min read

Learn how banks can strengthen cybersecurity, comply with regulations, and mitigate vendor risks with proven third-party cyber risk best practices.

Why Third Party Risk Management needs AI. How Genesis is Leading The Way

Why Third Party Risk Management needs AI. How Genesis is Leading The Way

Syed AmozSyed Amoz

May 2025 · 5 min read

Explore why AI is essential in third-party risk management and how Genesis Platform is pioneering the future of smart, automated TPRM.

How to Build a NIS2 Ready Third-Party Risk Program.

How to Build a NIS2 Ready Third-Party Risk Program.

Tanay RaiTanay Rai

April 2025 · 5 min read

Step-by-step guide to building a NIS2‑ready third-party risk program: meet EU cybersecurity mandates and secure your vendor ecosystem.

How to Manage Third-Party Risk with the Help of FFIEC Guidelines.

How to Manage Third-Party Risk with the Help of FFIEC Guidelines.

Tanay RaiTanay Rai

April 2025 · 5 min read

Navigate third-party risk using FFIEC guidelines: learn practical steps to assess vendors, comply with US banking regulations, and reduce risk.

PCI DSS and Its Impact on Third Party Risk Management.

PCI DSS and Its Impact on Third Party Risk Management.

Tanay RaiTanay Rai

April 2025 · 6 min read

The Payment Card Industry Data Security Standard (PCI DSS) is a globally recognized set of controls and testing procedures developed by the PCI Security Standards Council (PCI SSC) to protect cardholder data.

HITRUST vs SOC 2: Key differences and which to choose.

HITRUST vs SOC 2: Key differences and which to choose.

Tanay RaiTanay Rai

April 2025 · 6 min read

Explore the differences between HITRUST and SOC 2 compliance frameworks to select the best fit for your organization.

What is HITRUST and Its Impact on Third Party Risk Management.

What is HITRUST and Its Impact on Third Party Risk Management.

Tanay RaiTanay Rai

March 2025 · 5 min read

Discover what HITRUST certification entails and how it enhances vendor oversight and mitigates third‑party cybersecurity risks.

What is PCI DSS Compliance and What's New in PCI DSS 4.0?

What is PCI DSS Compliance and What's New in PCI DSS 4.0?

Tanay RaiTanay Rai

February 2025 · 5 min read

Get up to speed on PCI DSS compliance, understand new v4.0 requirements and their implications for vendor data protection and merchant risk.

Understanding Third-Party Cyber Risk Management.

Understanding Third-Party Cyber Risk Management.

Tanay RaiTanay Rai

January 2025 · 5 min read

A primer on third‑party cyber risk: why it matters, core components, and how to build a resilient TPRM framework for secure outsourcing.

The Insomniac Games Data Breach

The Insomniac Games Data Breach

Tanay RaiTanay Rai

December 2024 · 2 min read

Review the Insomniac Games breach: exposed data, attack methods, and how third-party vendors and access controls played a role.

Third-Party Risk Management in the Energy Sector

Third-Party Risk Management in the Energy Sector

Tanay RaiTanay Rai

November 2024 · 5 min read

Learn best practices for third‑party risk in energy: address operational, cyber, ESG, and compliance risks across complex supply chains.

Third Party Risk Management for aviation industry

Third Party Risk Management for aviation industry

Tanay RaiTanay Rai

September 2024 · 3 min read

Explore aviation TPRM essentials: manage vendor security, operations, and compliance to reduce disruptions and safety incidents.

What is Digital Operational Resilience Act (DORA)?

What is Digital Operational Resilience Act (DORA)?

Tanay RaiTanay Rai

September 2024 · 4 min read

Discover the EU’s Digital Operational Resilience Act: ICT risk rules, incident reporting duties, and third-party oversight for financial firms.

What You Need to Know About SEBI's TPRM Updates

What You Need to Know About SEBI's TPRM Updates

Tanay RaiTanay Rai

August 2024 · 4 min read

Stay compliant with SEBI's latest TPRM updates: understand new requirements, timelines, and how to align your vendor risk frameworks.

SIEM vs IDS: What's The Difference?

SIEM vs IDS: What's The Difference?

Tanay RaiTanay Rai

August 2024 · 5 min read

Explore the key differences between SIEM and IDS—understand their roles, deployment ease, and how to choose the right tool for cybersecurity.

What is Third Party Risk Management Lifecycle?

What is Third Party Risk Management Lifecycle?

Tanay RaiTanay Rai

August 2024 · 6 min read

Learn the TPRM lifecycle: from risk identification and due diligence to continuous monitoring and risk remediation in third-party management.

Third Party Risk Management for Healthcare Sector

Third Party Risk Management for Healthcare Sector

Tanay RaiTanay Rai

July 2024 · 6 min read

Explore TPRM in healthcare: manage vendor compliance, data security, and patient safety through structured risk assessments and audits.

Third Party Risk Management for Banking and Finance Sector

Third Party Risk Management for Banking and Finance Sector

Tanay RaiTanay Rai

July 2024 · 6 min read

Implement TPRM in banking & finance: assess vendor risk, meet compliance mandates, and safeguard transactions and customer data.

Ultimate Cybersecurity and Compliance Guide for Small Businesses

Ultimate Cybersecurity and Compliance Guide for Small Businesses

Tanay RaiTanay Rai

June 2024 · 11 min read

Small business cybersecurity & compliance 101: learn essential controls, vendor vetting, and scalable ways to reduce risk on a budget.

How to assess vendor risk based on the relationship?

How to assess vendor risk based on the relationship?

Tanay RaiTanay Rai

June 2024 · 7 min read

Assess vendor risk by relationship type: learn when to apply basic checks vs. in-depth audits based on access, data and service criticality.

What is Third-Party Risk Management (TPRM) ? A Complete Guide (2024)

What is Third-Party Risk Management (TPRM) ? A Complete Guide (2024)

Syed AmozSyed Amoz

June 2024 · 4 min read

Complete guide to TPRM in 2024: understand frameworks, industry best practices, compliance drivers, and vendor risk strategies.

The Prudential Financial Data Breach

The Prudential Financial Data Breach

Tanay RaiTanay Rai

February 2024 · 2 min read

Dive into the Prudential breach: how it happened, affected stakeholders, and what TPRM and cybersecurity lessons organizations should not miss.

The 23andMe Data Breach

The 23andMe Data Breach

Tanay RaiTanay Rai

February 2024 · 2 min read

Analyze the 23andMe breach: what data was exposed, breach timeline, and how to mitigate genetic vendor risks in supply chains.

Orrick, Herrington & Sutcliffe Data Breach

Orrick, Herrington & Sutcliffe Data Breach

Tanay RaiTanay Rai

January 2024 · 2 min read

Explore the Orrick law firm data breach: root causes, impact on client confidentiality, and third-party oversight imperatives.

UnitedHealth Pays $22 Million To Ransomware Group

UnitedHealth Pays $22 Million To Ransomware Group

Tanay RaiTanay Rai

January 2024 · 2 min read

Analyzing UnitedHealth’s $22M ransomware payout: lessons learned, breach response strategies, and improving vendor cybersecurity resilience.

What is PCI DSS Compliance? Requirements & More

What is PCI DSS Compliance? Requirements & More

Syed AmozSyed Amoz

October 2023 · 2 min read

Get an in-depth look at PCI DSS compliance: its core requirements, updates, and critical guidance for protecting payment data across your vendor ecosystem.

What is FISMA Compliance?

What is FISMA Compliance?

Sohini Roy

May 2023 · 2 min read

Learn about FISMA compliance: federal cybersecurity requirements, agency responsibilities, and how organizations must secure information systems.

What is HIPAA Compliance?

What is HIPAA Compliance?

Sohini Roy

April 2023 · 2 min read

Understand HIPAA compliance essentials: how to protect health data, enforce privacy rules, audit vendors, and avoid steep penalties.

What is Business Email Compromise (BEC)?

What is Business Email Compromise (BEC)?

Sohini Roy

April 2023 · 2 min read

Explore Business Email Compromise (BEC): how attackers trick employees, the financial impact, and tactics to defend against email fraud.

What is Cyber Risk Quantification?

What is Cyber Risk Quantification?

Sohini Roy

April 2023 · 2 min read

Discover cyber risk quantification: use data-driven models to measure financial impact, prioritize controls, and make informed security investments.

What is Shadow IT?

What is Shadow IT?

Sohini Roy

April 2023 · 2 min read

Learn about Shadow IT: hidden apps and devices in your environment—why they introduce risk and how to discover and manage them effectively.

What is DNS Hijacking?

What is DNS Hijacking?

Sohini Roy

February 2023 · 2 min read

Understand DNS hijacking: how attackers redirect your traffic, the consequences, and protective steps like DNSSEC to prevent tampering.

What is Zero Trust Security?

What is Zero Trust Security?

Sohini Roy

February 2023 · 2 min read

Explore Zero Trust security: never trust internal or external actors, enforce authentication per session, and reduce risk across your network.

What is Spear Phishing?

What is Spear Phishing?

Tanay RaiTanay Rai

January 2023 · 1 min read

Understand spear phishing: targeted email-based social engineering—learn how attackers operate and how to detect and prevent these threats.

What is Ransomware as a Service (RaaS)?

What is Ransomware as a Service (RaaS)?

Tanay RaiTanay Rai

January 2023 · 2 min read

Learn about Ransomware‑as‑a‑Service: how affiliates rent malware, its risks to businesses, and essential prevention tactics.

What is Cyber Resilience?

What is Cyber Resilience?

Tanay RaiTanay Rai

December 2022 · 2 min read

Explore cyber resilience: bounce back from attacks, build adaptive defenses, and ensure continuity in the face of threats.

Threats Faced by Banking and Finance

Threats Faced by Banking and Finance

Tanay RaiTanay Rai

December 2022 · 2 min read

Discover top cyber and operational threats in banking/finance—from fraud to ransomware—and how firms are mitigating risk.

Penetration Testing: A Comprehensive Guide

Penetration Testing: A Comprehensive Guide

Tanay RaiTanay Rai

December 2022 · 2 min read

Comprehensive guide to penetration testing: phases, methodologies, tools, and how to use pen tests to strengthen your security.

Medibank Data Breach: What Happened and Lessons Learned

Medibank Data Breach: What Happened and Lessons Learned

Tanay RaiTanay Rai

November 2022 · 2 min read

Analyze the Medibank breach: sensitive health data exposed, response steps, and key takeaways for vendor cybersecurity practices.

What is CIS Control Framework?

What is CIS Control Framework?

Sohini Roy

November 2022 · 2 min read

Learn the CIS Control Framework: 18 essential security practices, from asset management to incident response, for strong defenses.

What is DNSSEC?

What is DNSSEC?

Tanay RaiTanay Rai

November 2022 · 2 min read

Understand DNSSEC: how it secures DNS lookups, prevents cache poisoning, and why it’s essential for domain integrity.

Vulnerabilities of OpenSSL 3

Vulnerabilities of OpenSSL 3

Tanay RaiTanay Rai

November 2022 · 2 min read

Discover known vulnerabilities in OpenSSL 3: their impact, patch recommendations, and best practices to secure cryptographic libraries.

What is Patch Management?

What is Patch Management?

Tanay RaiTanay Rai

November 2022 · 1 min read

Master patch management: streamline updates, close vulnerabilities, and build vendor processes with automated patching programs.

What is the MITRE ATT&CK Framework?

What is the MITRE ATT&CK Framework?

Tanay RaiTanay Rai

October 2022 · 2 min read

Explore MITRE ATT&CK: the adversary tactics and techniques matrix used to enhance detection, threat modeling, and defence strategies.

What is SIG Questionnaire?

What is SIG Questionnaire?

Tanay RaiTanay Rai

October 2022 · 1 min read

Get a primer on SIG questionnaires: standardized security assessments that streamline vendor audits and due diligence.

What is Cache Poisoning?

What is Cache Poisoning?

Sohini Roy

October 2022 · 1 min read

Discover how DNS cache poisoning manipulates DNS responses, its risks, and how DNSSEC and validation guard against these attacks.

What is a DMARC Record?

What is a DMARC Record?

Sohini Roy

October 2022 · 1 min read

Understand DMARC records: email authentication, how they prevent spoofing, and why enforcing DMARC protects brand and recipients.

What is GDPR Compliance?

What is GDPR Compliance?

Sohini Roy

October 2022 · 2 min read

The General Data Protection Regulation (GDPR) is an EU law that came into effect on May 25th, aiming to protect personal data and regulate how organizations handle information.

Lapsus$ Cyberattack on Okta: What You Need to Know

Lapsus$ Cyberattack on Okta: What You Need to Know

Sohini Roy

September 2022 · 2 min read

Coverage of the Lapsus$ hack on Okta: how the breach happened, risks from compromised MFA tokens, and mitigation strategies.

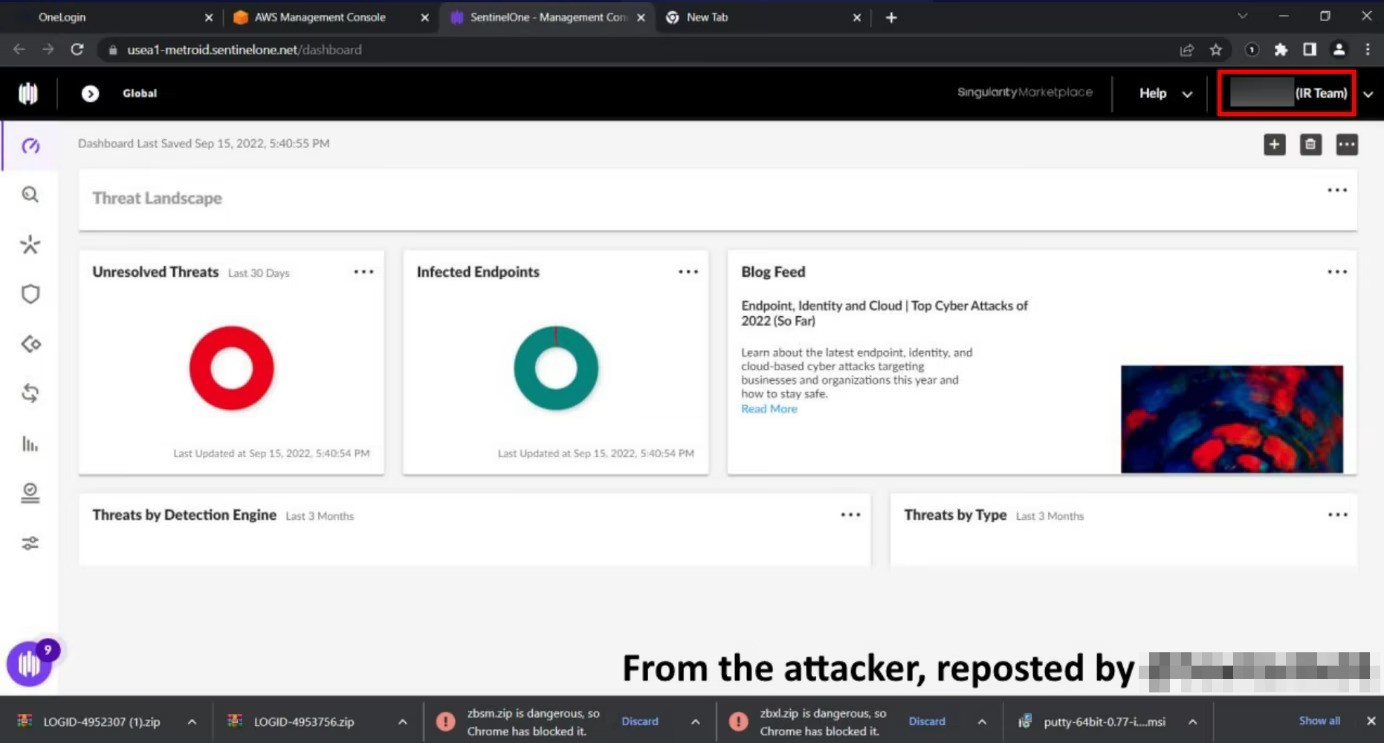
10,000 Okta Credentials Compromised: What You Need to Know

10,000 Okta Credentials Compromised: What You Need to Know

Sohini Roy

September 2022 · 2 min read

Learn about the leak of 10,000 Okta credentials, its impact on enterprise access, and how to harden identity systems post-incident.

Uber Hacked by 18-Year-Old in 2022

Uber Hacked by 18-Year-Old in 2022

Sohini Roy

September 2022 · 2 min read

Learn about Uber’s 2022 security breach by a teen hacker: stolen data, exploited systems, and how to strengthen identity and access controls.

What is DNS?

What is DNS?

Sohini Roy

July 2022 · 2 min read

Learn how DNS works like the internet’s phonebook—translating domain names to IPs, caching responses, and enabling web browsing at scale.

What is Genesis Platform? Overview of the Platform

What is Genesis Platform? Overview of the Platform

Syed AmozSyed Amoz

June 2022 · 1 min read

Explore Genesis Platform’s third-party risk management features: AI‑powered assessments, compliance monitoring, and vendor oversight.

What is Attack Surface Management?

What is Attack Surface Management?

Sohini Roy

June 2022 · 2 min read

Learn attack surface management: discover external digital threats, prioritize asset protection, and continuously monitor exposures.

What is Third-Party Risk Management (TPRM)?

What is Third-Party Risk Management (TPRM)?

Sohini Roy

June 2022 · 2 min read

Complete guide to TPRM: understand its framework, why it matters, and how to manage vendor risks across cyber, compliance, and operational domains.

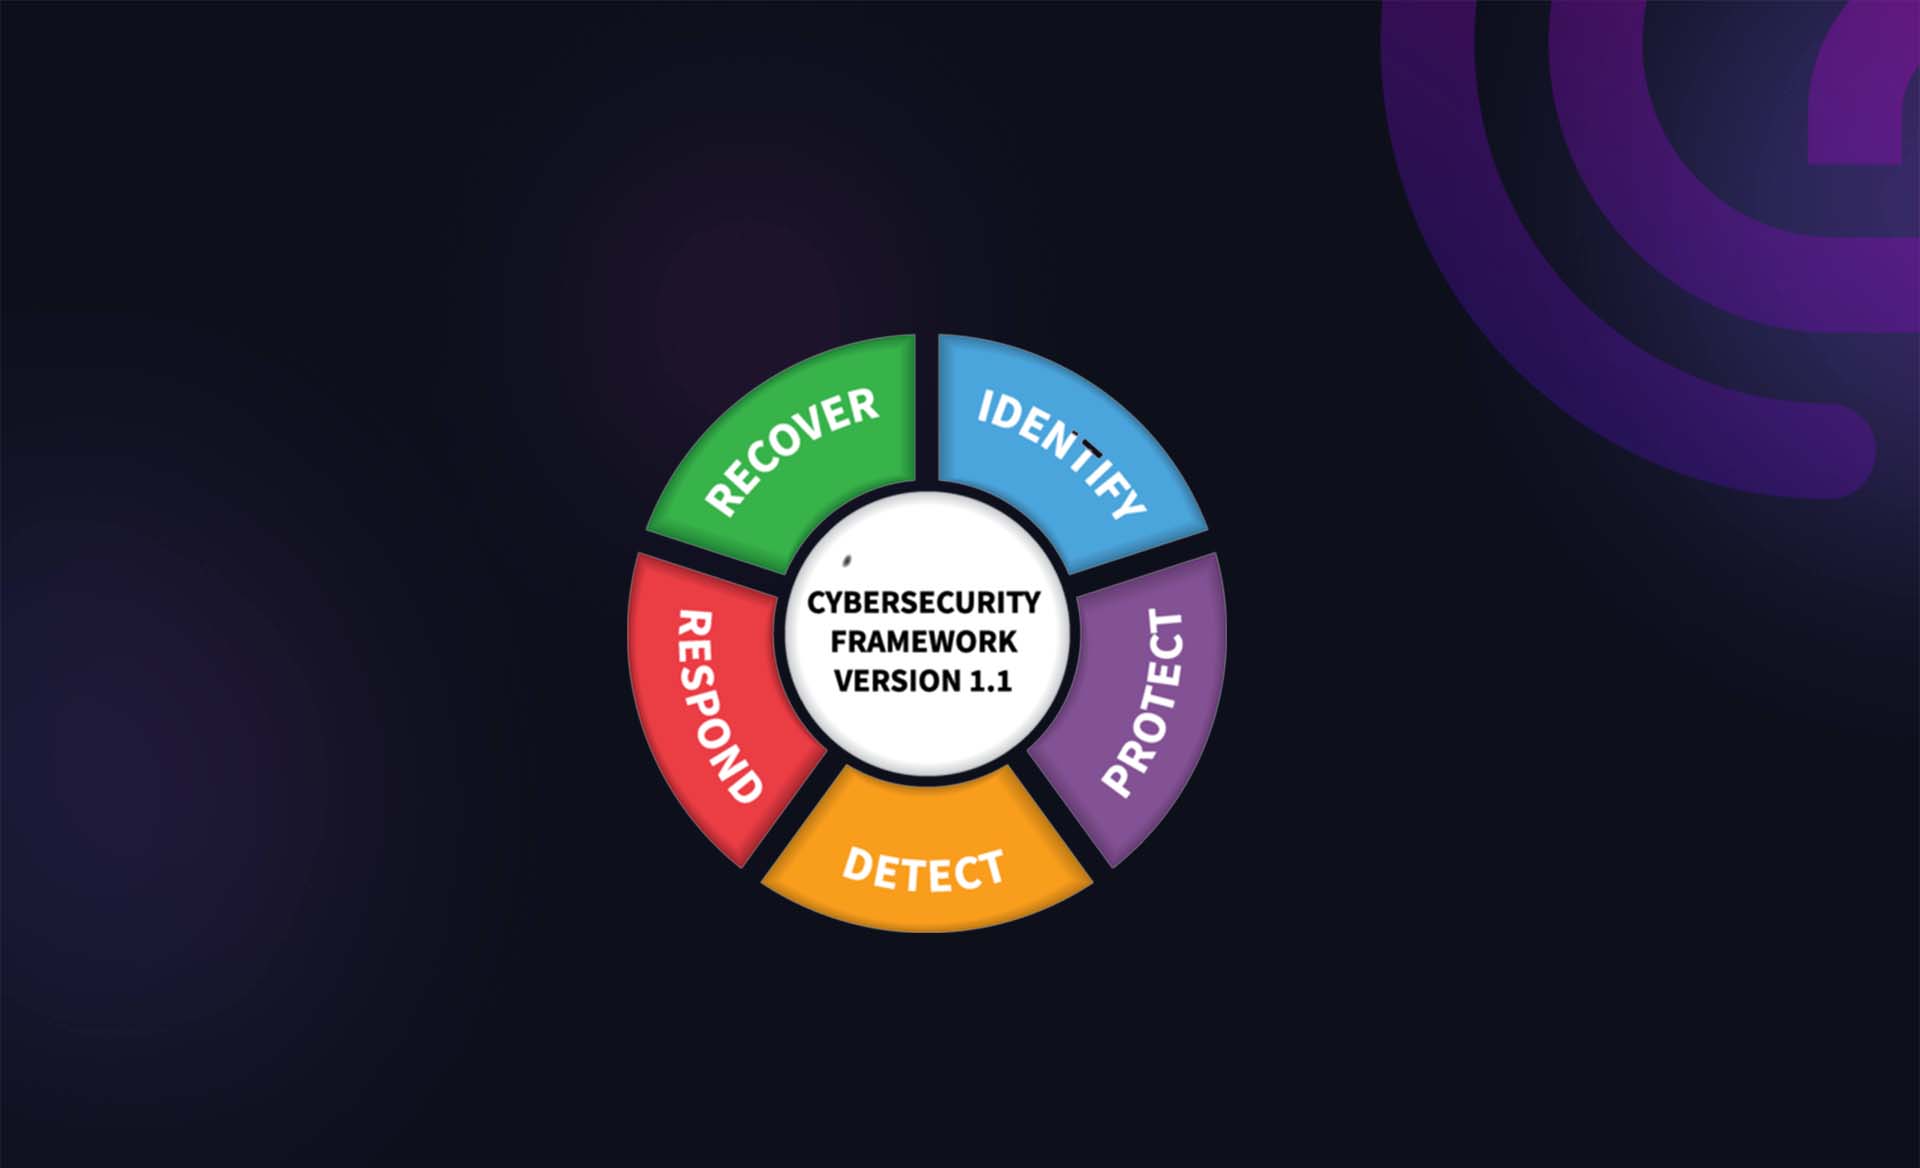
What is the NIST Cybersecurity Framework?

What is the NIST Cybersecurity Framework?

Sohini Roy

June 2022 · 2 min read

Learn the NIST Cybersecurity Framework: explore the five core functions—Identify, Protect, Detect, Respond, Recover—for cyber resilience.