Sohini Roy
Contributor to the Merqab risk intelligence blog.
Writing on Compliance, Cybersecurity, TPRM, Breach Analysis.
Published perspectives
16 articles
What is FISMA Compliance?
Learn about FISMA compliance: federal cybersecurity requirements, agency responsibilities, and how organizations must secure information systems.
Read article
What is HIPAA Compliance?
Understand HIPAA compliance essentials: how to protect health data, enforce privacy rules, audit vendors, and avoid steep penalties.
Read article
What is Business Email Compromise (BEC)?
Explore Business Email Compromise (BEC): how attackers trick employees, the financial impact, and tactics to defend against email fraud.
Read article
What is Cyber Risk Quantification?
Discover cyber risk quantification: use data-driven models to measure financial impact, prioritize controls, and make informed security investments.
Read article
What is Shadow IT?
Learn about Shadow IT: hidden apps and devices in your environment—why they introduce risk and how to discover and manage them effectively.
Read article
What is DNS Hijacking?
Understand DNS hijacking: how attackers redirect your traffic, the consequences, and protective steps like DNSSEC to prevent tampering.
Read article
What is Zero Trust Security?
Explore Zero Trust security: never trust internal or external actors, enforce authentication per session, and reduce risk across your network.
Read article
What is CIS Control Framework?
Learn the CIS Control Framework: 18 essential security practices, from asset management to incident response, for strong defenses.
Read article
What is Cache Poisoning?
Discover how DNS cache poisoning manipulates DNS responses, its risks, and how DNSSEC and validation guard against these attacks.
Read article
What is a DMARC Record?
Understand DMARC records: email authentication, how they prevent spoofing, and why enforcing DMARC protects brand and recipients.
Read article
What is GDPR Compliance?
The General Data Protection Regulation (GDPR) is an EU law that came into effect on May 25th, aiming to protect personal data and regulate how organizations handle information.
Read article
Lapsus$ Cyberattack on Okta: What You Need to Know
Coverage of the Lapsus$ hack on Okta: how the breach happened, risks from compromised MFA tokens, and mitigation strategies.
Read article
10,000 Okta Credentials Compromised: What You Need to Know
Learn about the leak of 10,000 Okta credentials, its impact on enterprise access, and how to harden identity systems post-incident.
Read article
Uber Hacked by 18-Year-Old in 2022
Learn about Uber’s 2022 security breach by a teen hacker: stolen data, exploited systems, and how to strengthen identity and access controls.
Read article
What is DNS?
Learn how DNS works like the internet’s phonebook—translating domain names to IPs, caching responses, and enabling web browsing at scale.
Read article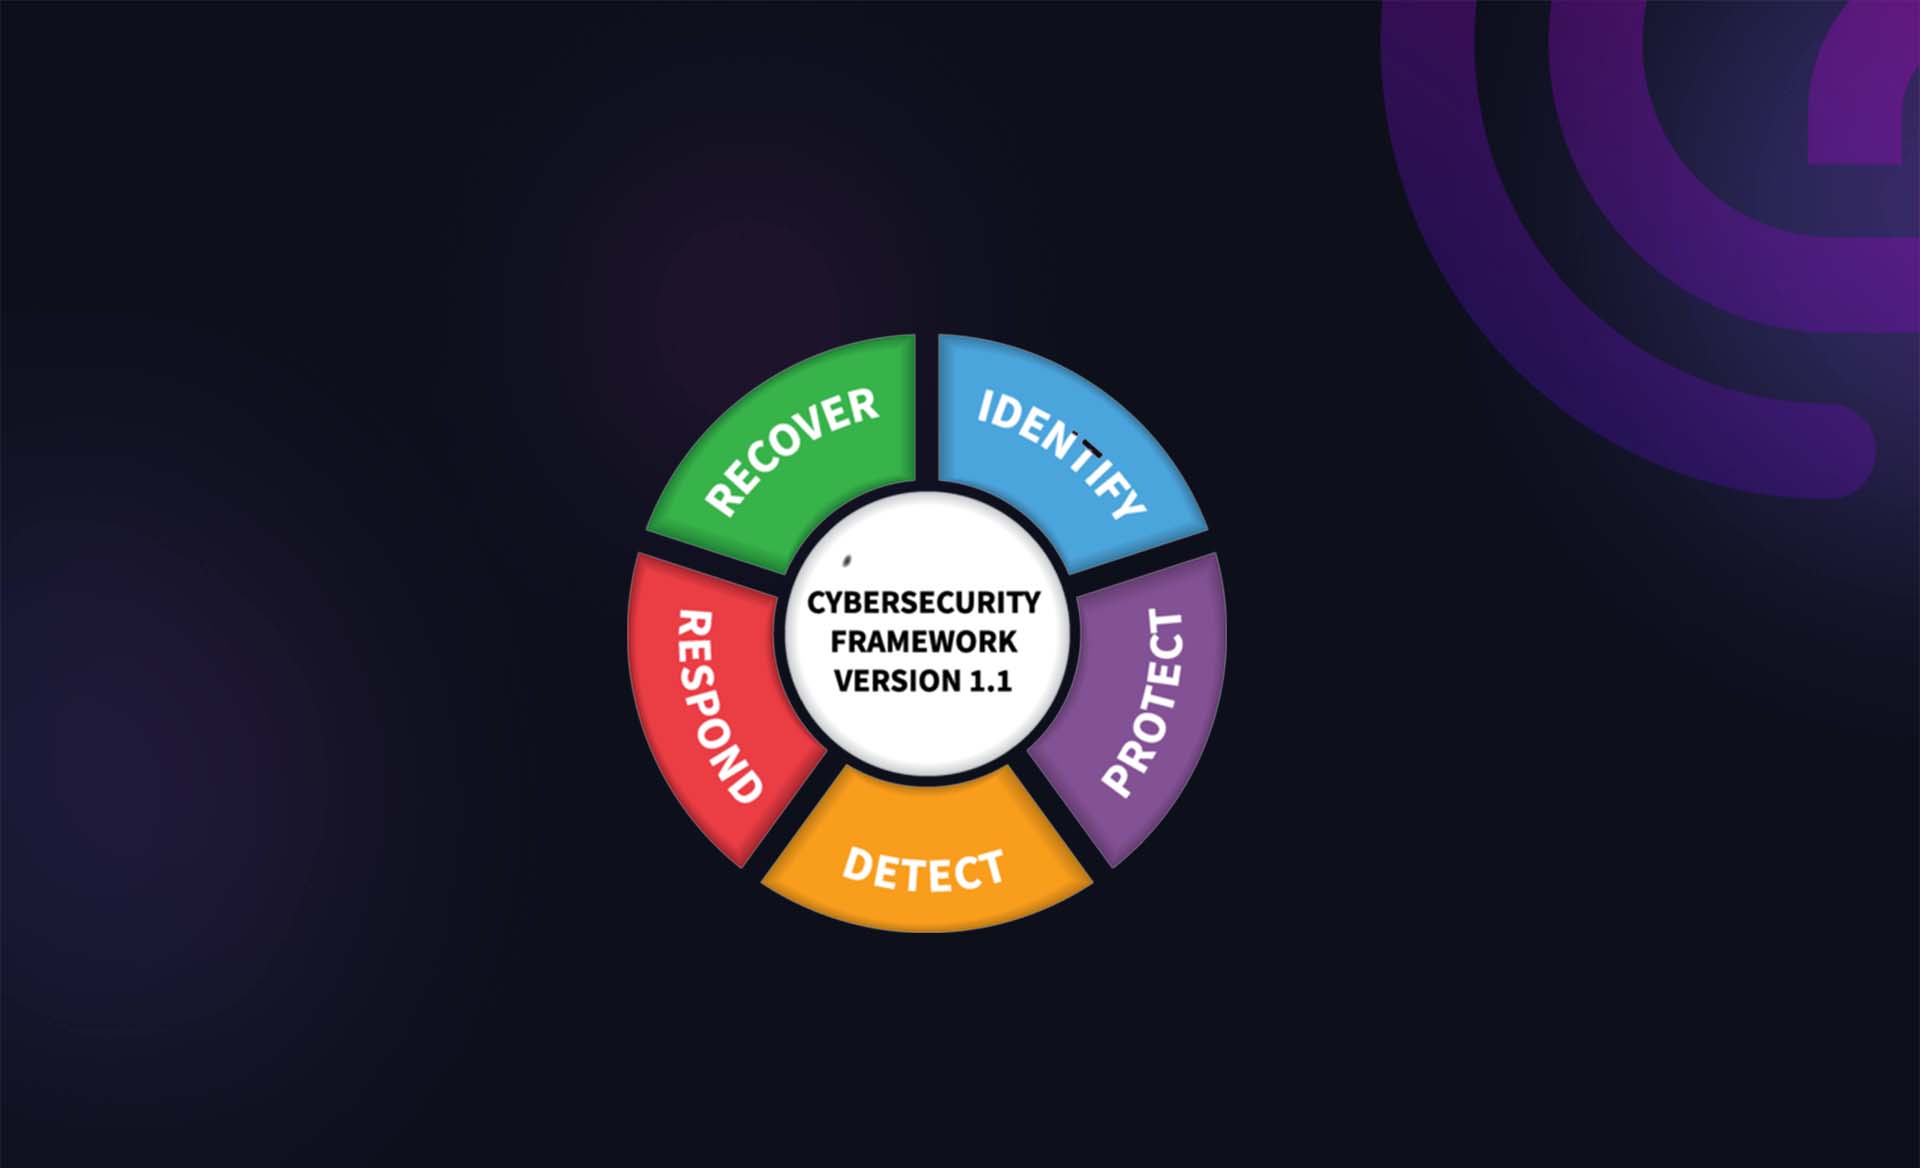
What is the NIST Cybersecurity Framework?
Learn the NIST Cybersecurity Framework: explore the five core functions—Identify, Protect, Detect, Respond, Recover—for cyber resilience.
Read article